unsafe.ltd

evor

Vulnerability operations, from first finding to closed audit item.

Evor brings findings from every tool into one queue and moves each one to an owner, a fix and proof that it is fixed. Here is what that looks like.

Request an Evor demo

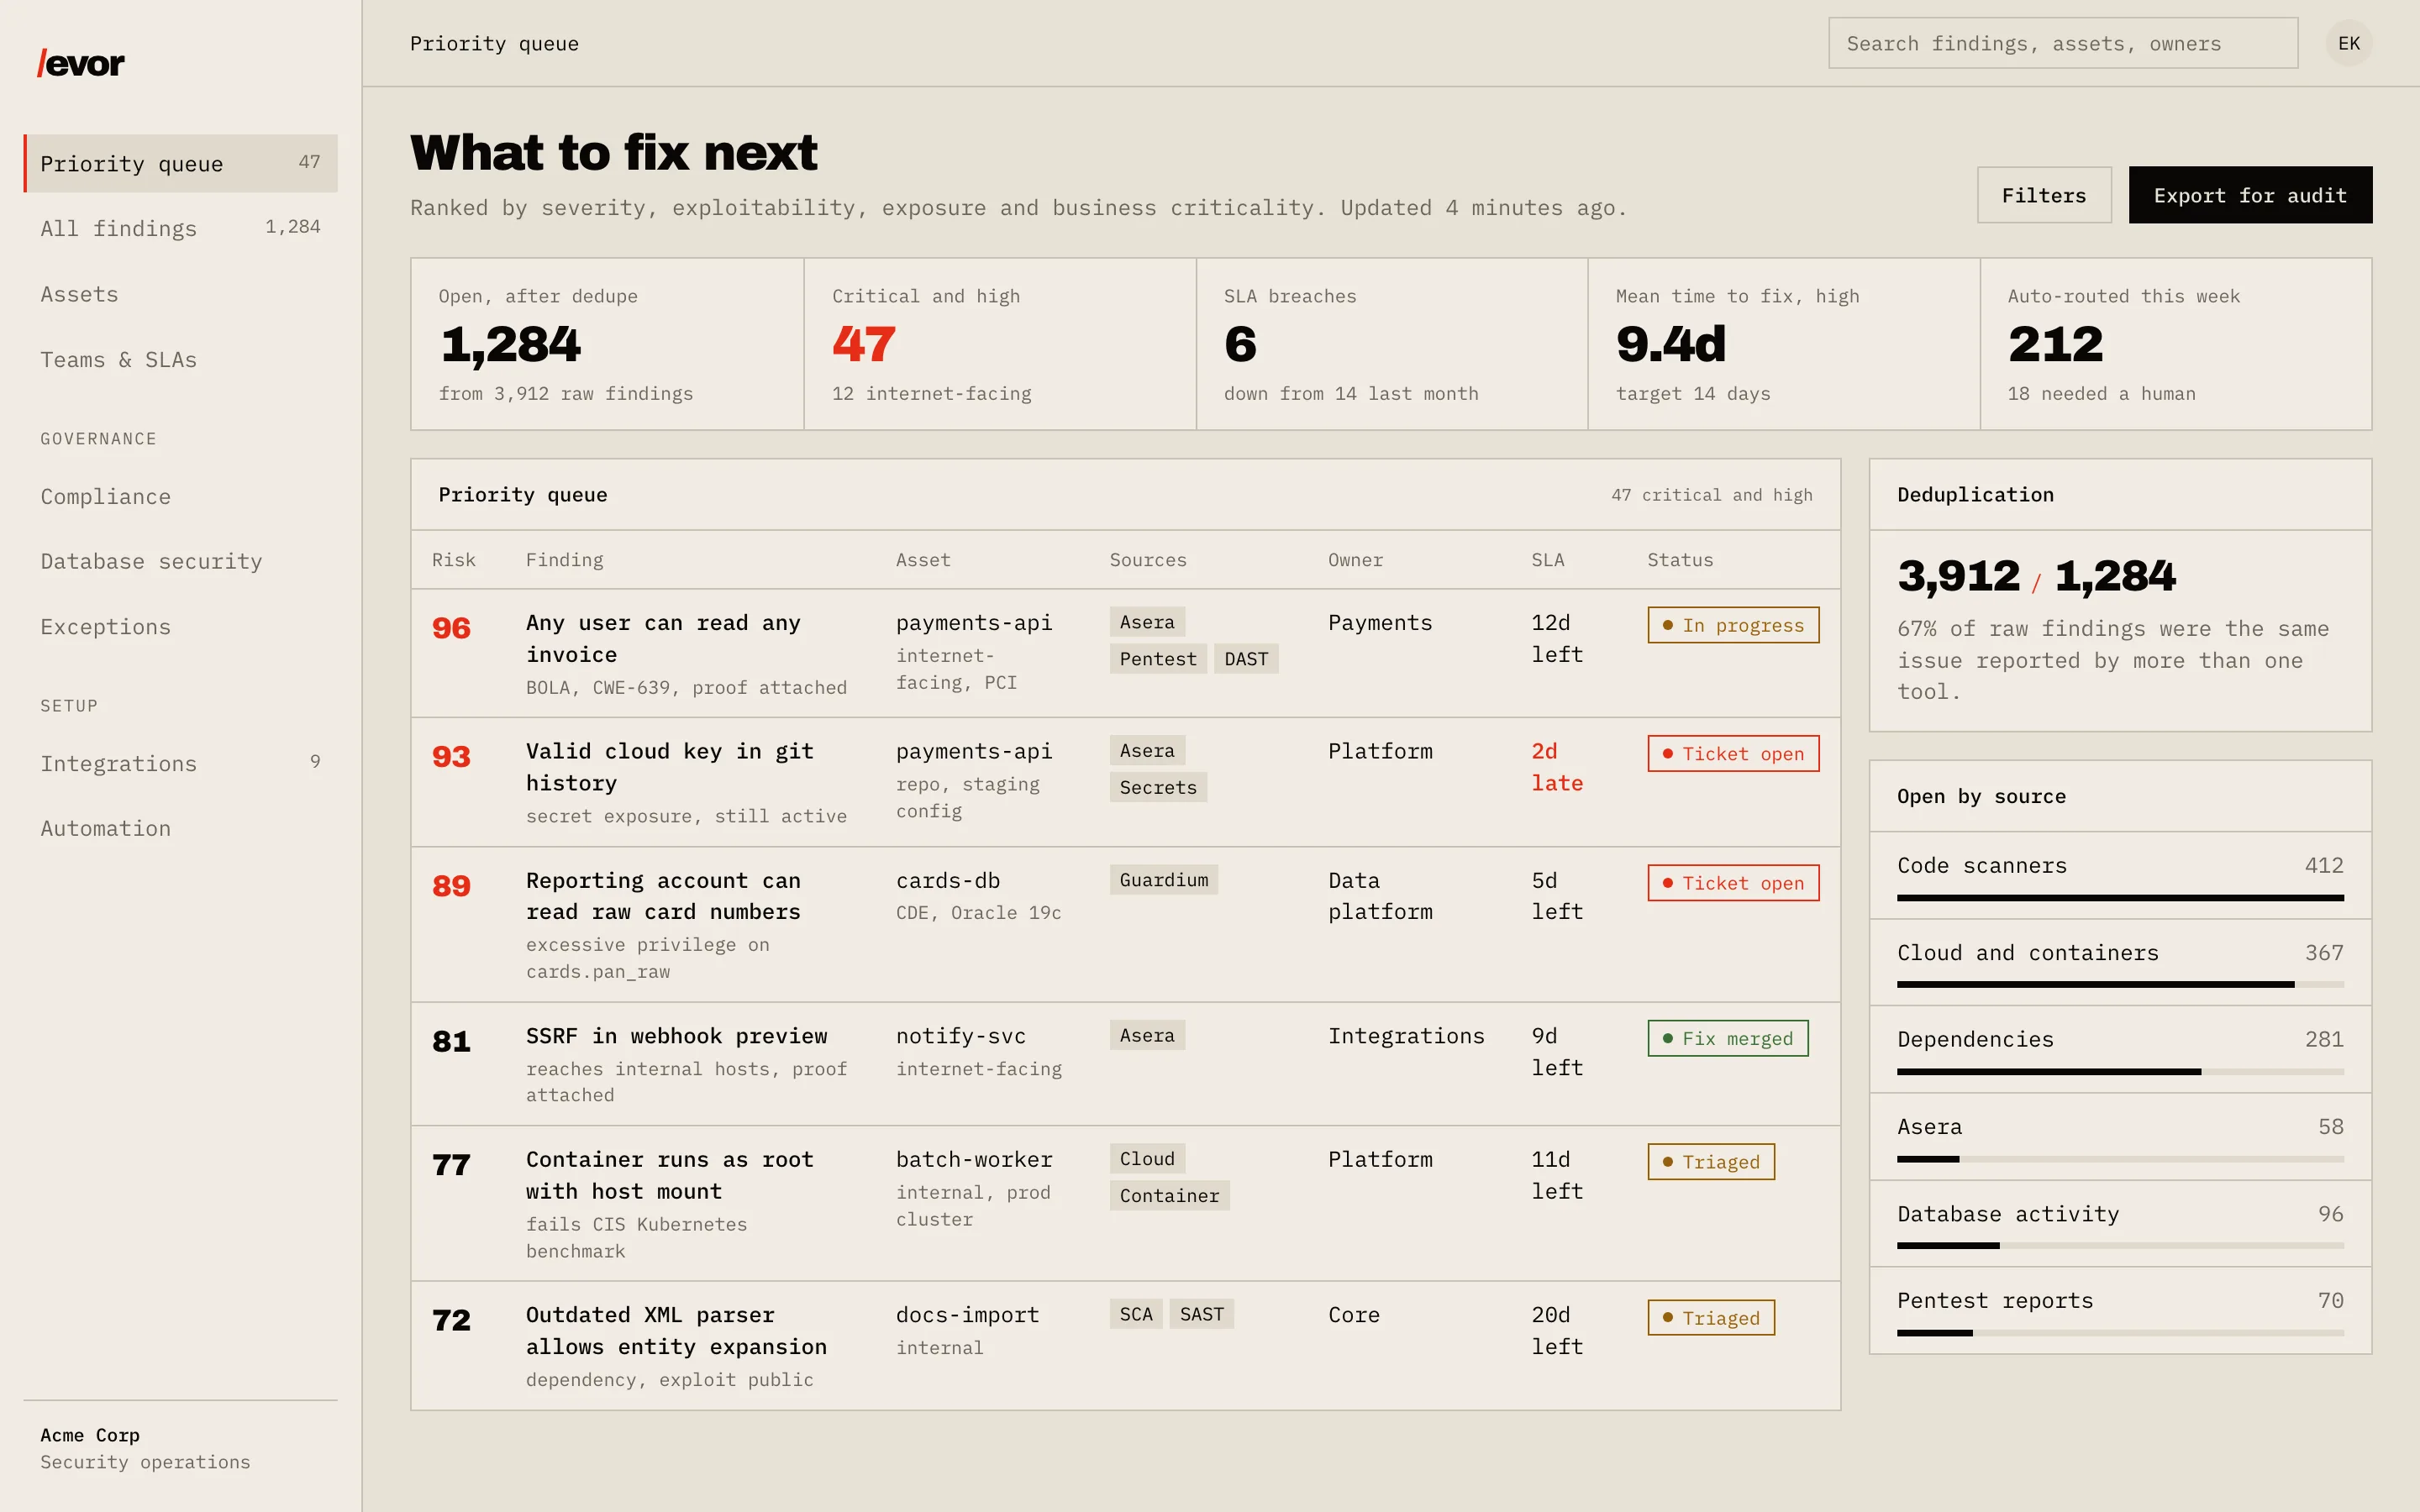
One queue for every finding.

Evor pulls findings from scanners, pentest reports, cloud tools, database monitoring and Asera, merges duplicates and ranks what is left by real risk.

  • Deduplicated against the assets they affect
  • An owner and an SLA on every item
  • Risk from severity, exploitability, exposure and asset value
Evor priority queue: deduplicated findings from several tools ranked by risk, with owners, SLAs and status

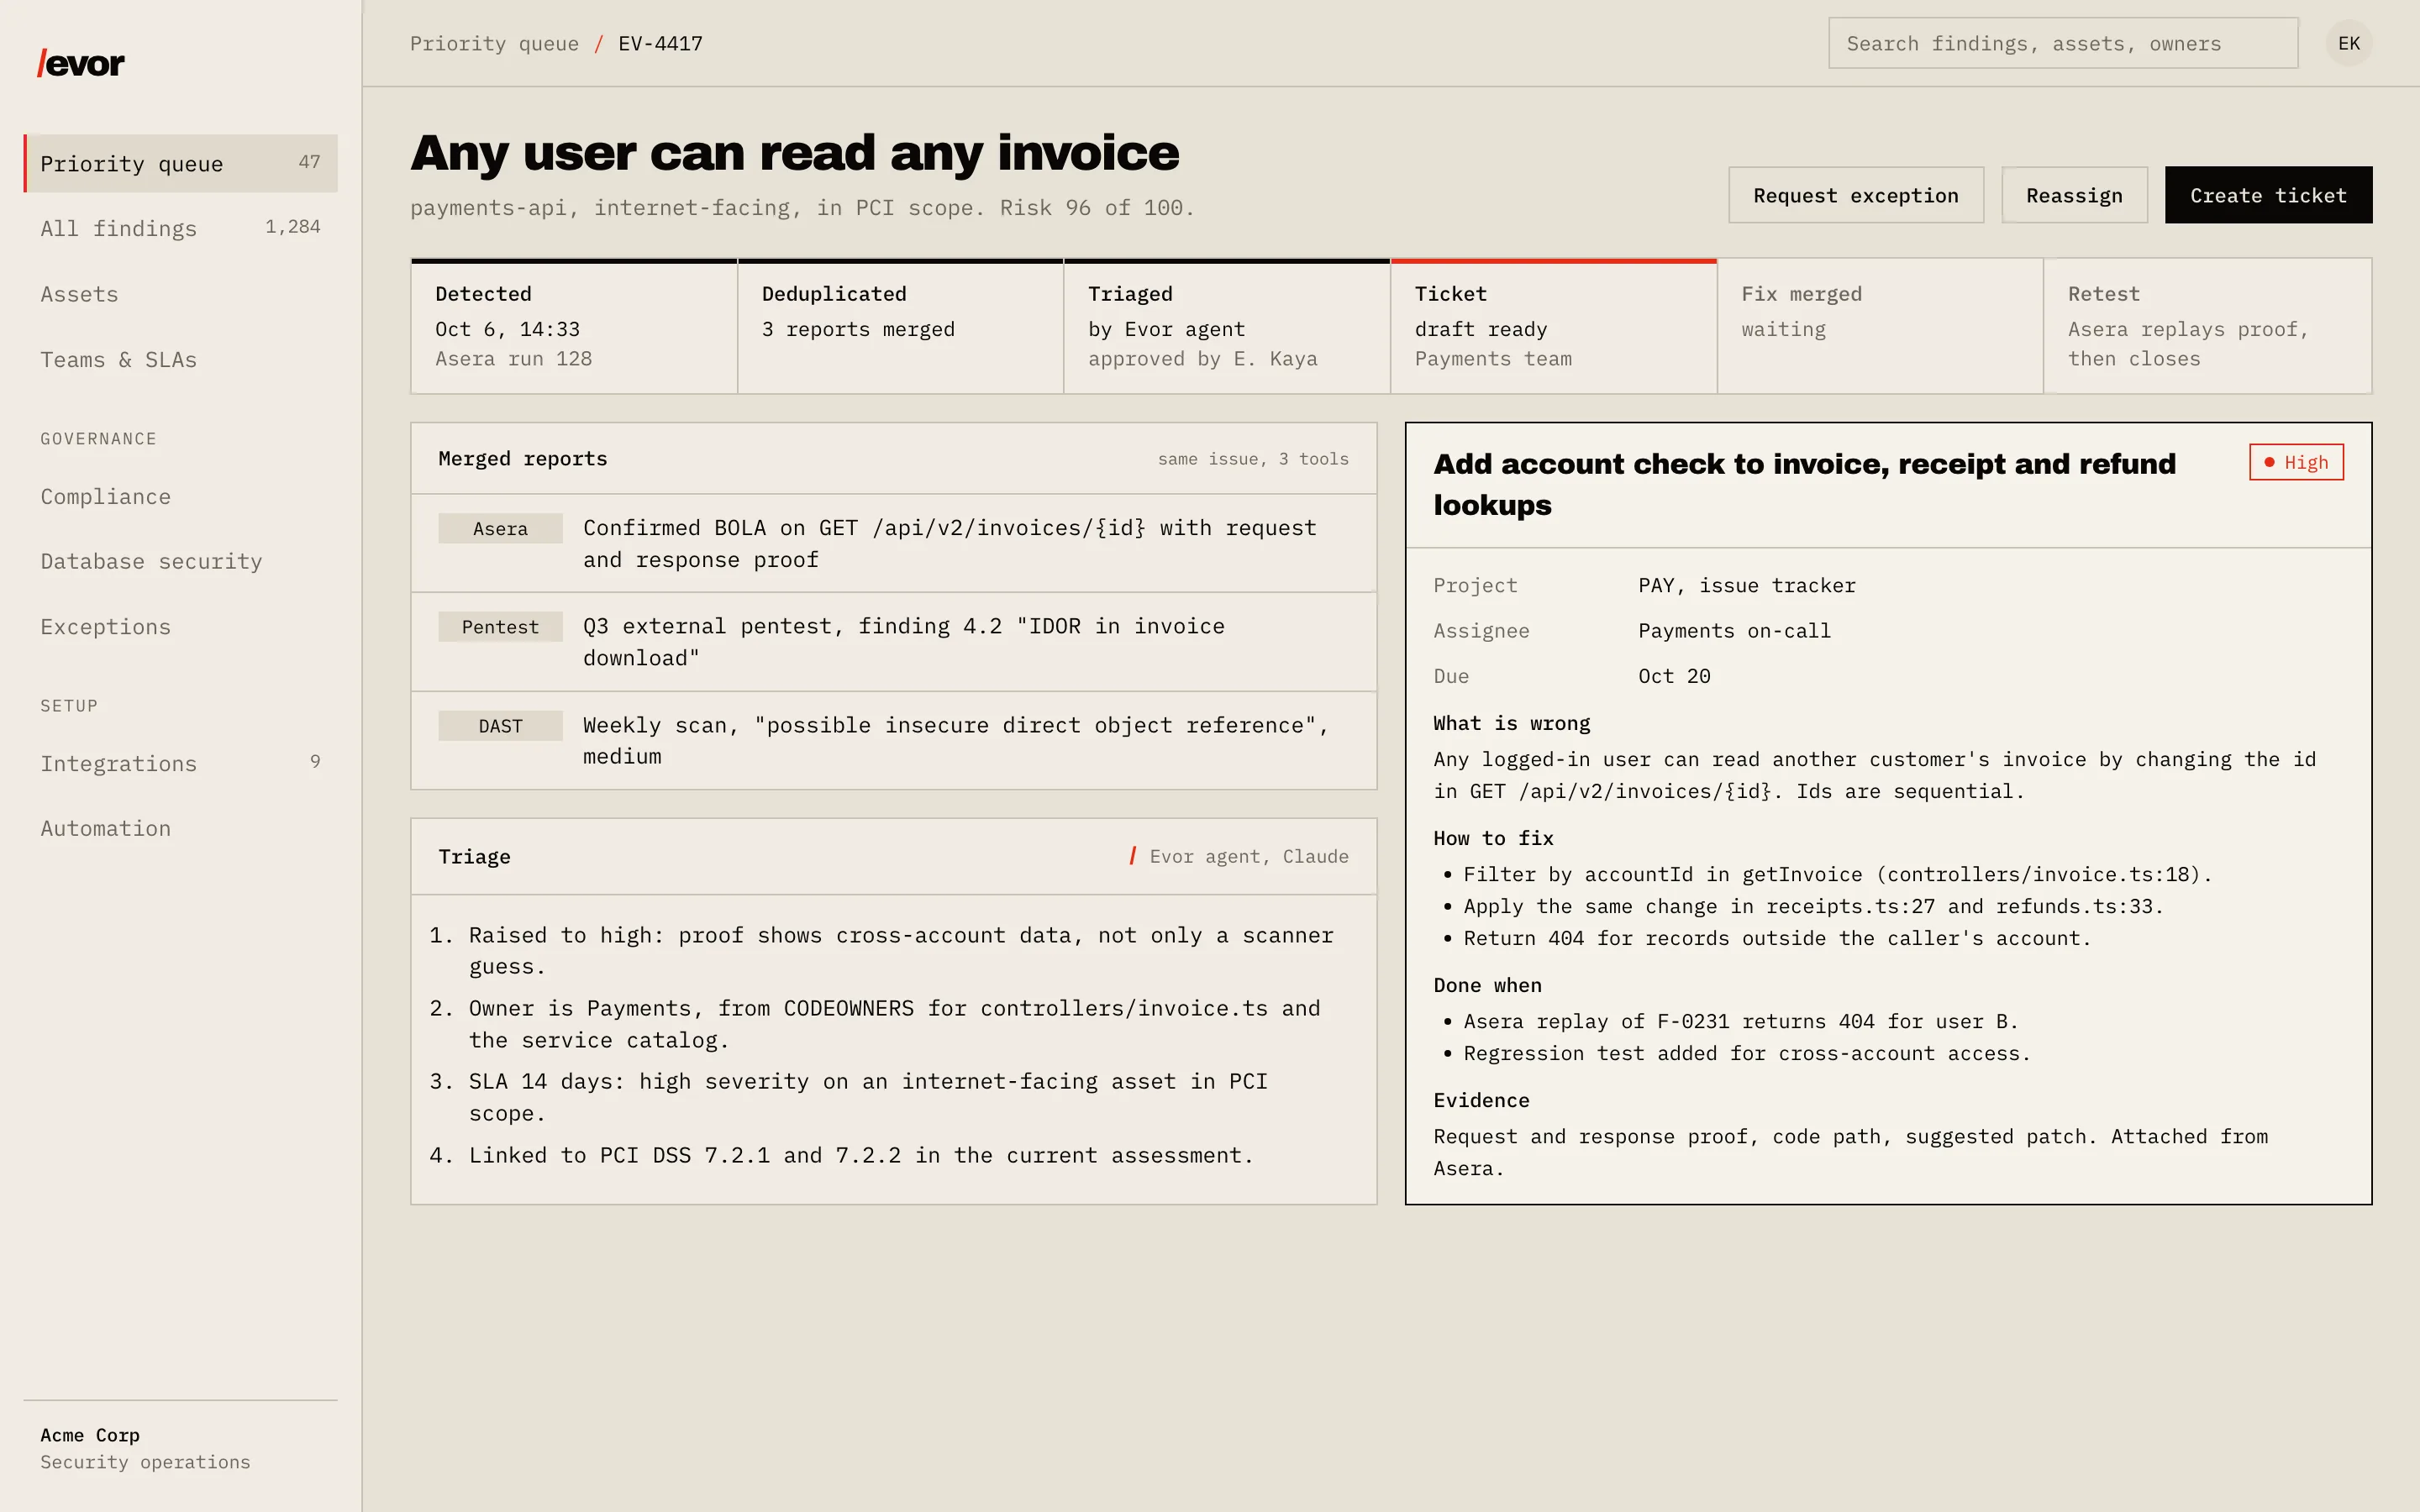
From finding to ticket, without the busywork.

An LLM agent triages each finding, explains its reasoning, finds the owning team and drafts a ticket with fix steps and evidence. After the fix, Asera retests and Evor closes it.

  • Reasons shown for every decision
  • Exceptions with an expiry date and an approver
  • Works with enterprise or local models
Evor handoff screen: three merged reports, AI triage reasons and a drafted ticket with fix steps

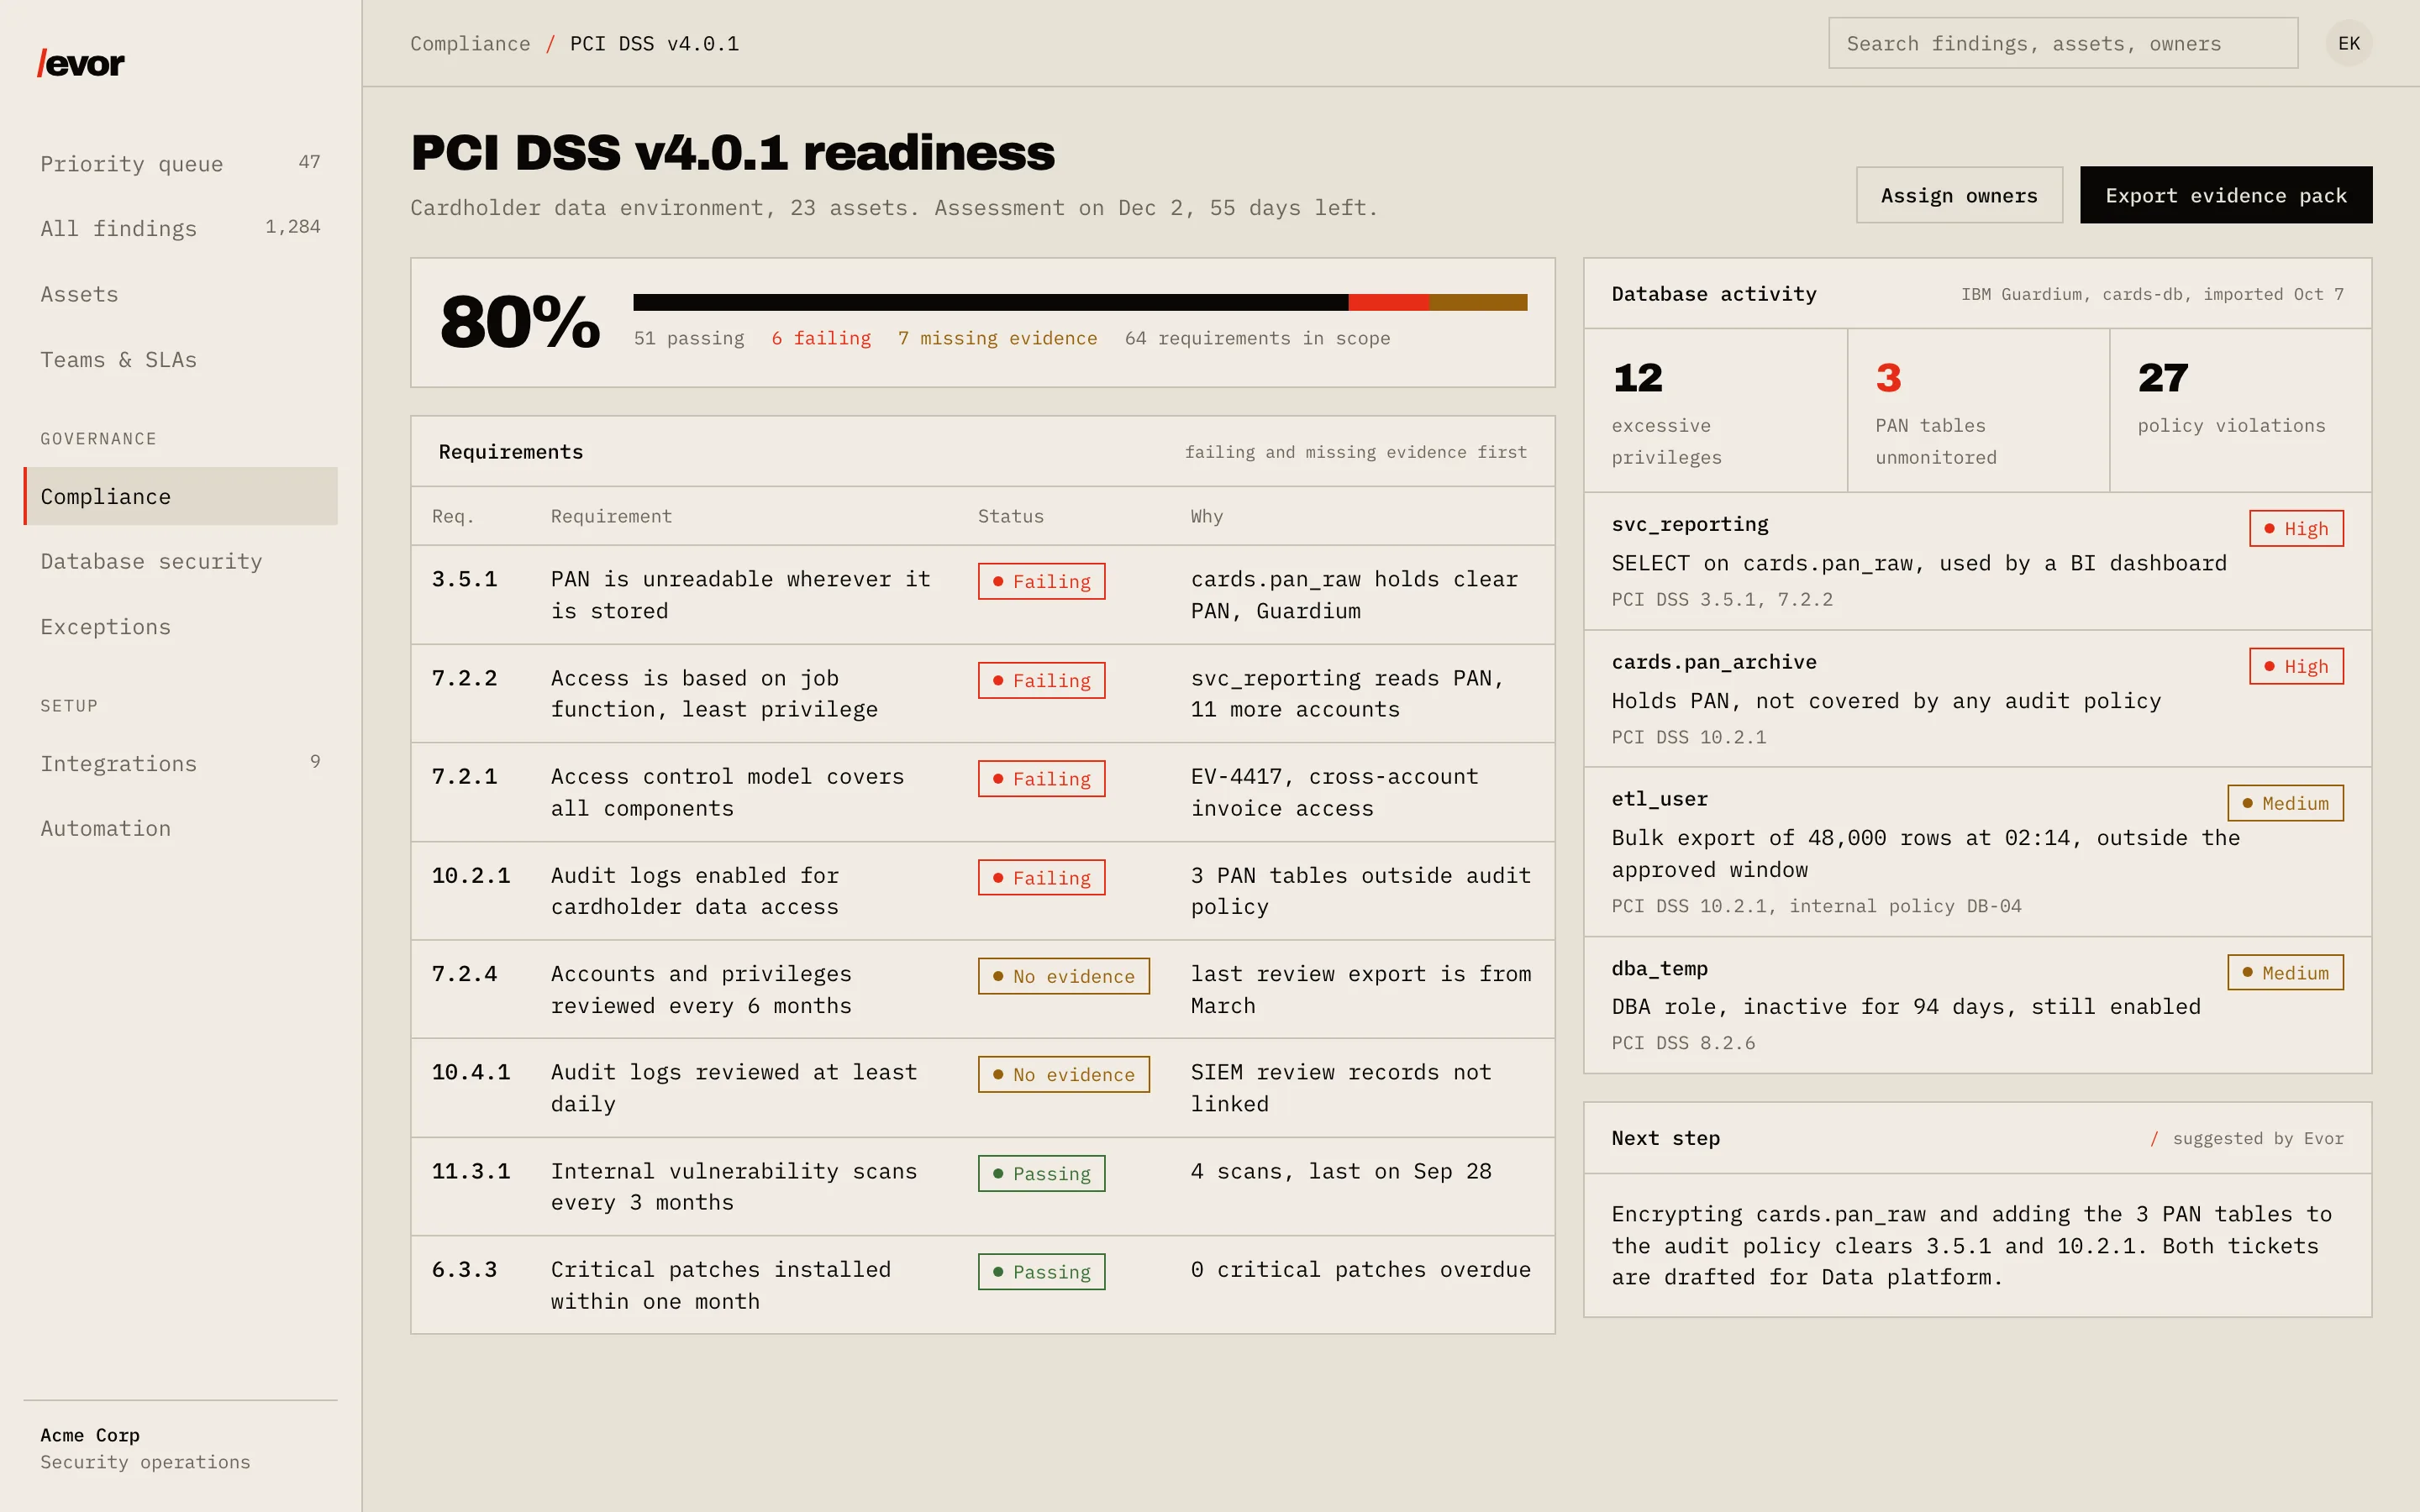
Know where you stand before the audit.

Evor maps findings and controls to PCI DSS v4.0.1 requirements, imports database activity reports from IBM Guardium and shows what is failing, which evidence is missing and what to fix first.

  • Excessive privileges and unmonitored sensitive tables
  • Evidence pack export for the assessor
  • Also ISO 27001, SOC 2, KVKK and GDPR
Evor PCI DSS readiness screen: requirement status with Guardium database findings mapped to requirements

Interface previews. All data shown is fictional.

Bring every finding into one place.

We are onboarding a small number of security and compliance teams. Write to us to connect your tools in a pilot.

Next: Asera, the agents that find and prove issues